Compliance at Advisory Firm Relies on ‘Good Communication’
When Lee Richardson was growing up, he did not expect to become a chief risk and compliance officer. But he was always asking questions—to the point that his third-grade teacher limited him to just three questions a day in class. His inquisitiveness and drive to understand people’s motivations and intentions prepared him for his compliance work at Creative Planning LLC, as well as his earlier career at the Naval Audit Service, as a consultant for firms now known as PWC and Deloitte and a compliance examiner for the Securities and Exchange Commission.
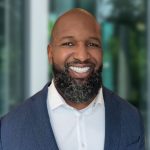
Lee Richardson
“My philosophy is that in all relationships, you need to have good communication,” Richardson says. “If you have good communication, then I think that goes a long way toward the health of the organization.”
Richardson spoke with PLANADVISER about how he handles compliance work at Creative Planning and weighs in on how he handles his job amid the rise of artificial intelligence. The interview has been edited for length.
PLANADVISER: What’s your recommended approach to compliance?
Lee Richardson: I think a lot of compliance officers lead with “no,” which I think is not helpful, but leading with “yes” is not smart. So we try to lead with listening. When you approach a situation and all you see is negative, you get to a point where the people will stop asking you questions. They will start to ask for forgiveness rather than ask for permission.
At the SEC, whenever somebody had a question, most of the time the response was, “What are the facts and circumstances?” In this space, it’s really important to make sure that you have an understanding of what the actual question is and what people are trying to do. If you can just stop, breathe and ask follow-up questions and understand what the objective is, then you can be part of the solution.
PLANADVISER: What might advisers not understand about the compliance process?
Richardson: A lot of times, as compliance officers, there is this fear that the organization is going to do something they shouldn’t do. Whenever you operate from a place of fear, you’re trying to protect the organization, but everything that is coming out is almost negative.
I wish [compliance officers] could take a step back and just think, “What is the best way to help my organization try to make the right choice?” Sometimes there are places where the compliance officers don’t really have that opportunity because they don’t have a seat at the table. [At] Creative Planning, I truly have a seat at the table and the compliance department here is truly respected. So we have great relationships around the organization, and that’s very beneficial.
PLANADVISER: Is there an average day at your job?
Richardson: I don’t think there is an average day. From a risk and compliance perspective, there are so many things that the team is touching on. If you’re in the [human resources] department, you’re dealing with employee matters. If you’re a wealth manager, you’re dealing with client matters. We have other business roles dealing with other businesses. The compliance department is in all three of those, pretty heavily. But then we do things with clients, like if clients are going through a divorce, or if a client has diminished capacity. We have a lot of business relationships that also require a compliance review as well. It’s a lot of those things every day.
PLANADVISER: Given increasing use of artificial intelligence, how are you making sure your advisers are using it responsibly?
Richardson: A big part of all this is creating the right level of awareness and making sure that the workforce is aware of these types of risks and what their responsibilities continue to be. Because these are not new responsibilities. If you’re the adviser and you’re providing advice, whether you got that from [non-AI] Google or from the library or Claude, you’re responsible for what you’re saying to the client.
So [I’m] trying not to overly focus on the technology, but focus on the process and what we [are] delivering to the client. The thing that I get concerned with is if someone is going to take that [AI] output and not review it, [then] they’re not going to understand it, and … they’re going to provide that to a client. That exposes us to risk.
From an enterprise level, there’s a lot of controls that we have in place now to reduce the risk of people doing things that they should not be doing. We have a cybersecurity director, Matt Norton, who likes to [say] that AI tools [are] essentially like going from giving the employees a shovel to giving them a bulldozer. There is a lot more damage that can be done with the bulldozer, obviously, than you can do with the shovel. A lot more good can be done as well, but it has to be used the right way.
PLANADVISER: How would you respond if someone argued that an AI-powered “compliance bot” could replace human compliance officers?
Richardson: I think a program would definitely be helpful, but there are going to be points where you need to have human experience and some emotional intelligence—particularly if you have a business discussion and there’s not a clear-cut path, and there are different people in the room who have different perspectives. Being able to say, “This is what the regulation is saying, and here’s how you could apply that in this particular situation,” and then advis[ing] the group on different things to try to find solutions—I just don’t think you’re going to get that with the bot.